Manage EU AI Act compliance in one platform.
Meet the platform for end-to-end EU AI Act compliance. Classify, analyse, document and govern all your AI systems.
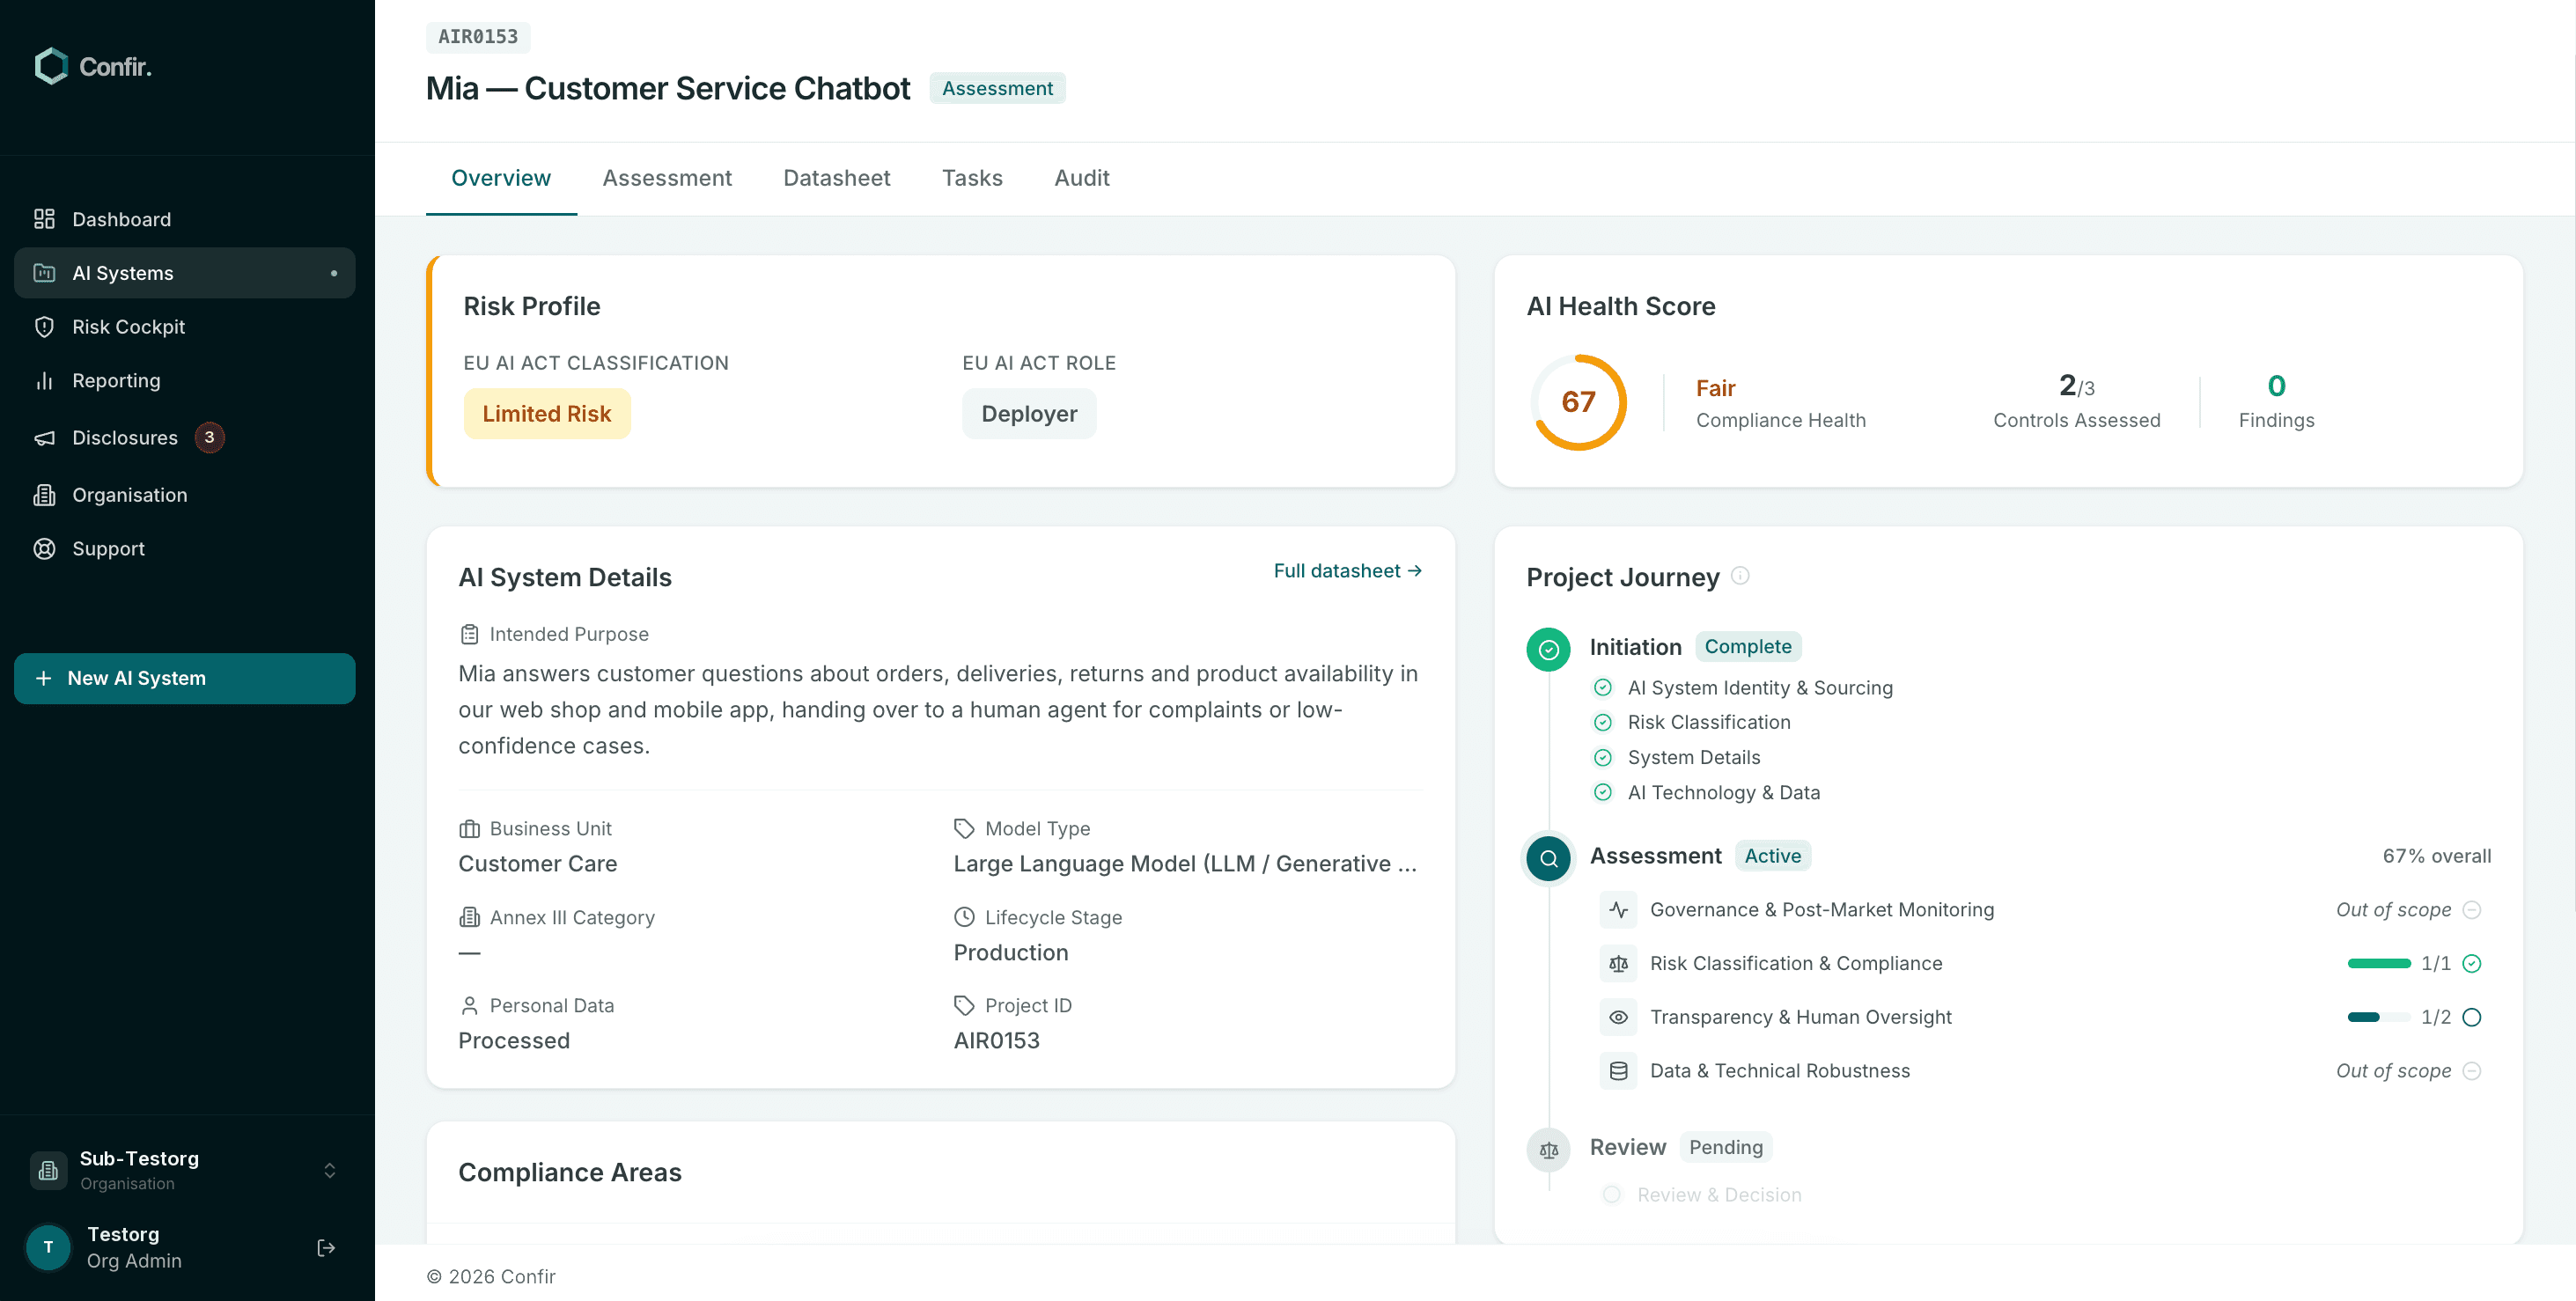
Four pillars to fully operationalise the EU AI Act.
One system of record, with every finding traced to the Article it rests on.
Compliance Workflows
Takes any AI system from first intake to a signed conformity package. Guided intake captures the system, the rule engine classifies it against Article 6 and Annex III, and the scoped four-area assessment carries it through to the Annex IV technical file.
One platform for every EU AI Act role and risk class.
Your obligations depend on who you are in the AI supply chain and how your system is classified. Confir resolves both automatically — scoping controls, surfacing gaps and generating the exact documentation your provider or deployer role requires for each risk class.
High
Risk
Limited
Risk
Minimal
Risk
Provider
Deployer
Importer
Distributor
Documentation Deliverables
Transparency Package
Fundamental Rights Impact Assessment
Declaration of Conformity
Annex IV technical file
Operational & reporting
Post-Market Monitoring
MSA Audit Export
Incident Reporting
EU database registration
Describe your AI system once. The rule engine maps every obligation.
Describe your AI system once and Confir determines which Articles apply, scopes the exact controls you need to assess, and pre-fills everything it can already derive.

Confir Intelligence
Deterministic rule engine
Automatic risk and role classification
Art. 6 · Annex III
Supply-chain role
Use case, sector and supply-chain role mapped to Article 6 and Annex III in seconds.
Auto-scoped compliance assessments
Scoped from 22 obligations
Auto-filled from intake
Only the controls that apply to your system. No generic compliance checklists.
Guided flows for every obligation
To the Article it implements
FRIA · Annex IV · DoC
Every datapoint flows through the assessment and into your documentation.
Run EU AI Act compliance in-house — without consultants.
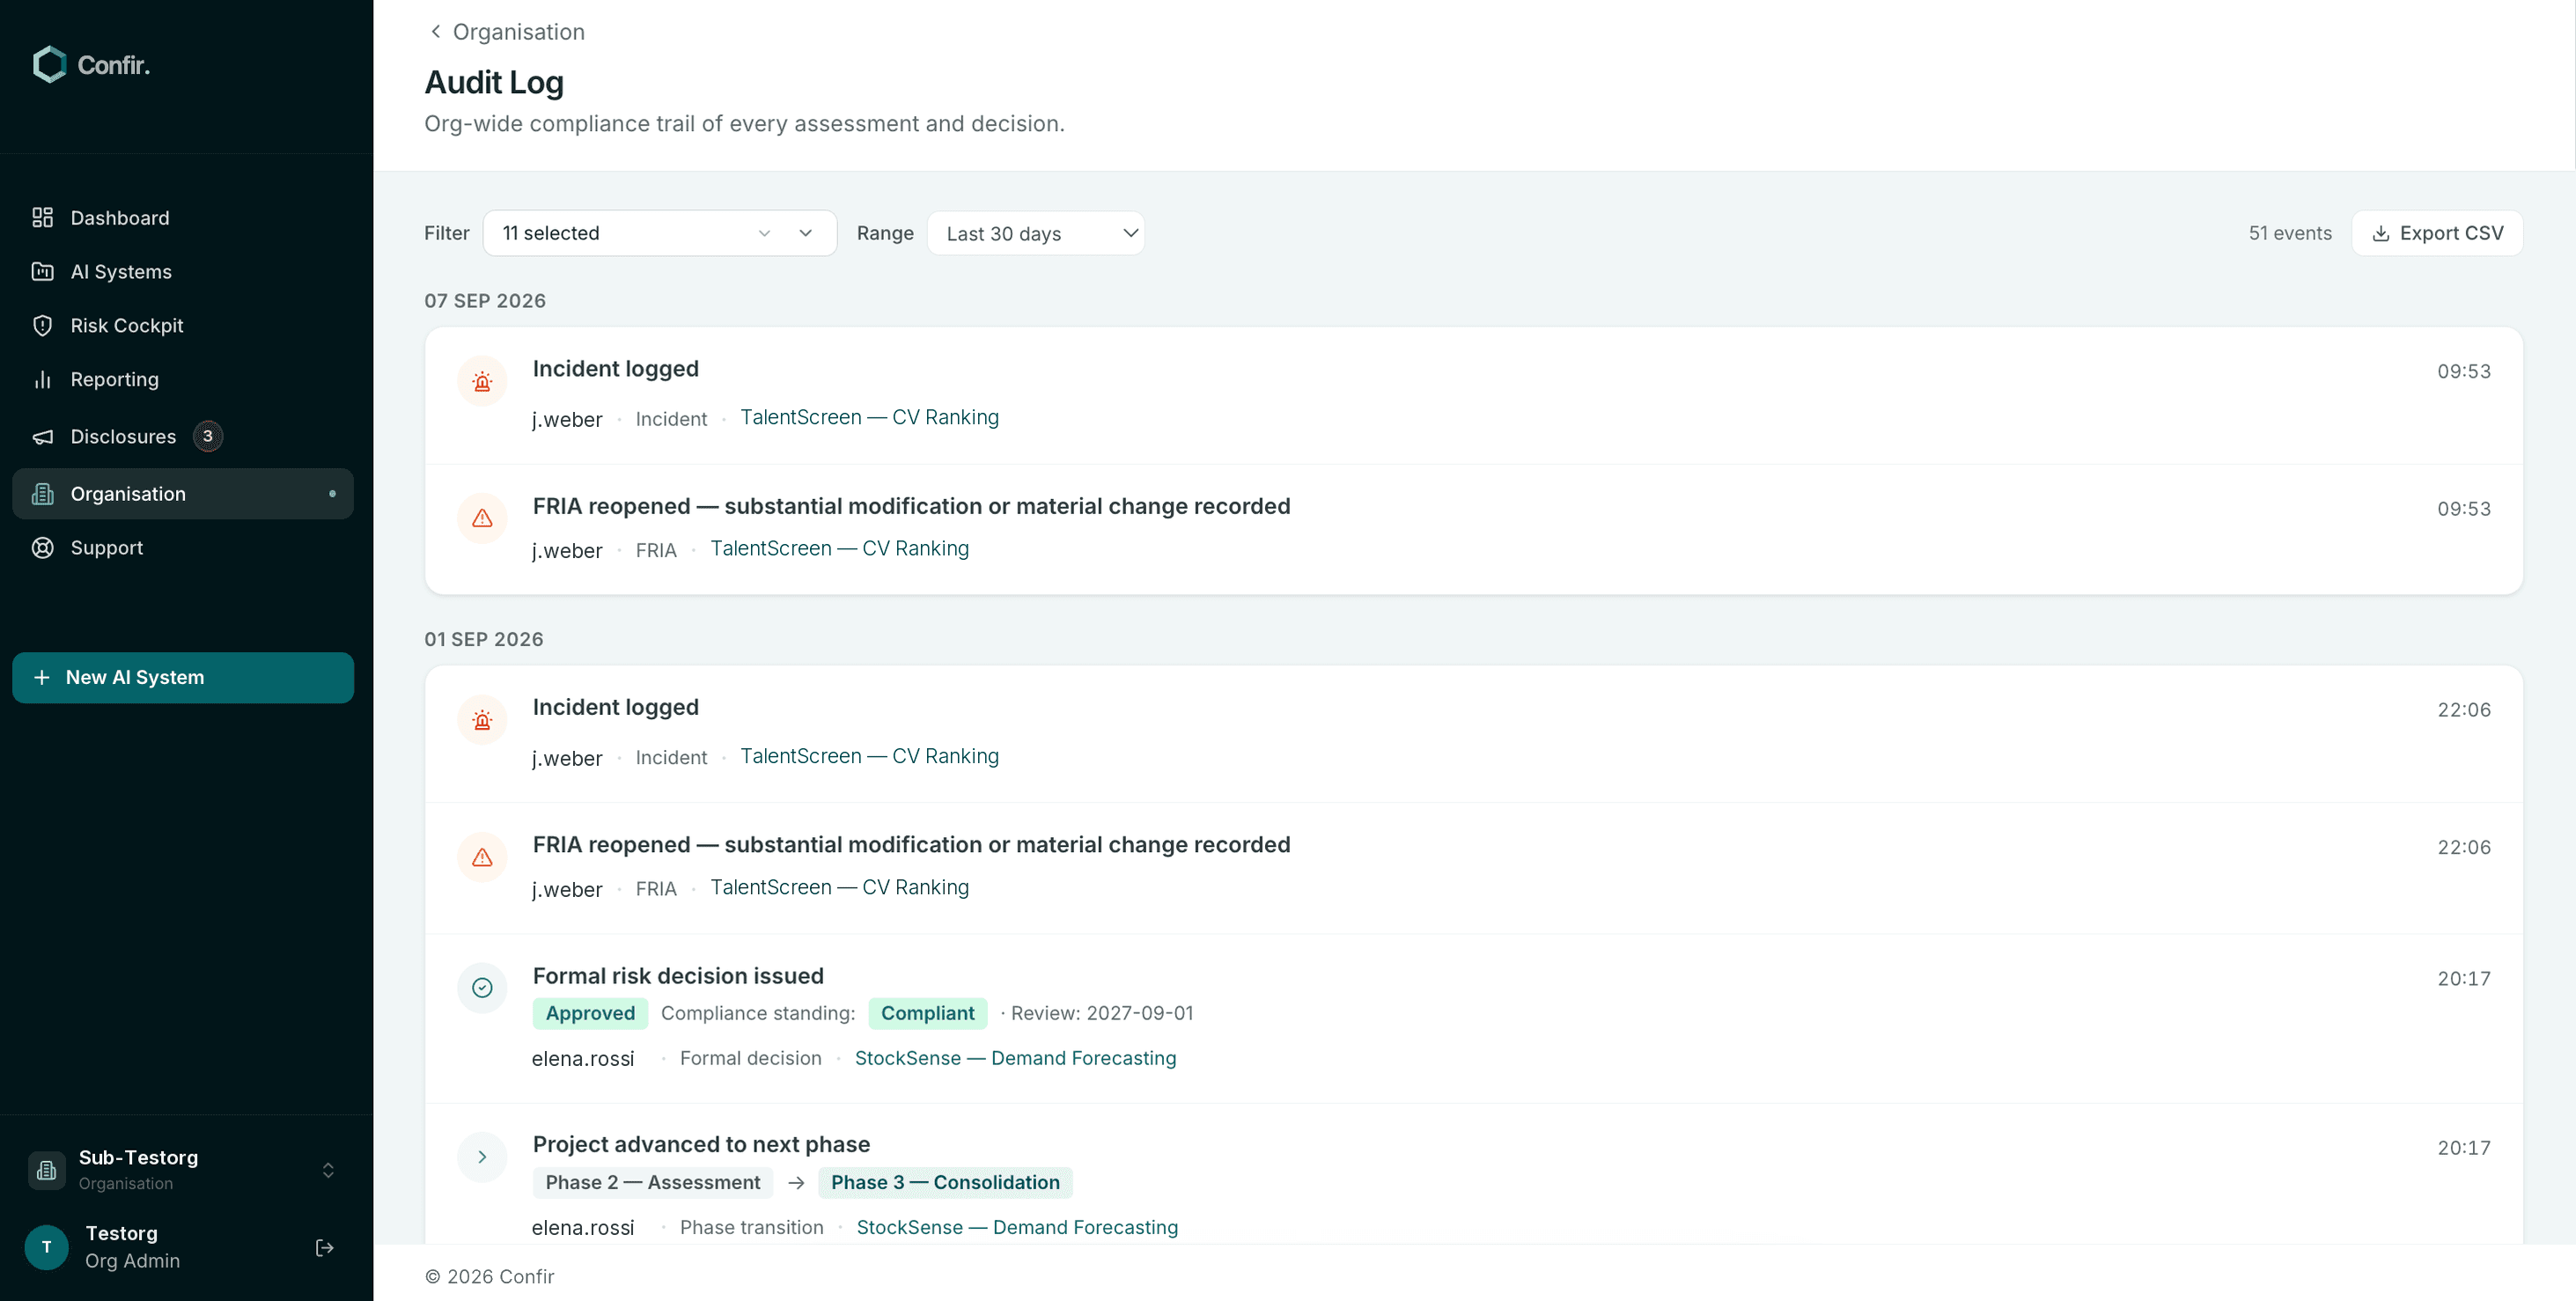
The regulation is encoded in the platform, so your team doesn't have to interpret it. Confir turns the EU AI Act into structured steps, auto-scoped controls and an audit trail a regulator can verify — no six-month consulting engagement, no black-box AI, no guesswork about which obligations apply.
to register your first AI system
Guided 4-step intake with helpful information at every step.
to complete a full assessment
Intake, classification, controls and review — end to end.
articles encoded in the rule engine
Plus all 13 annexes — every obligation traced to the exact EU AI Article.
Scoped controls & obligations
Only the controls that apply to your role and risk class. Answers pre-filled from intake, gaps asked as plain questions, every high-risk duty surfaced.
Guided high-risk workflows
Every high-risk obligation walked through step by step: FRIA, Annex IV technical documentation, the Declaration of Conformity and Article 50 transparency — pre-filled and cited to the Regulation.
Risk & Findings Management
Open findings tracked by severity, routed to owners, and closed with documented remediations. Your organisation's full AI risk posture in one cockpit.
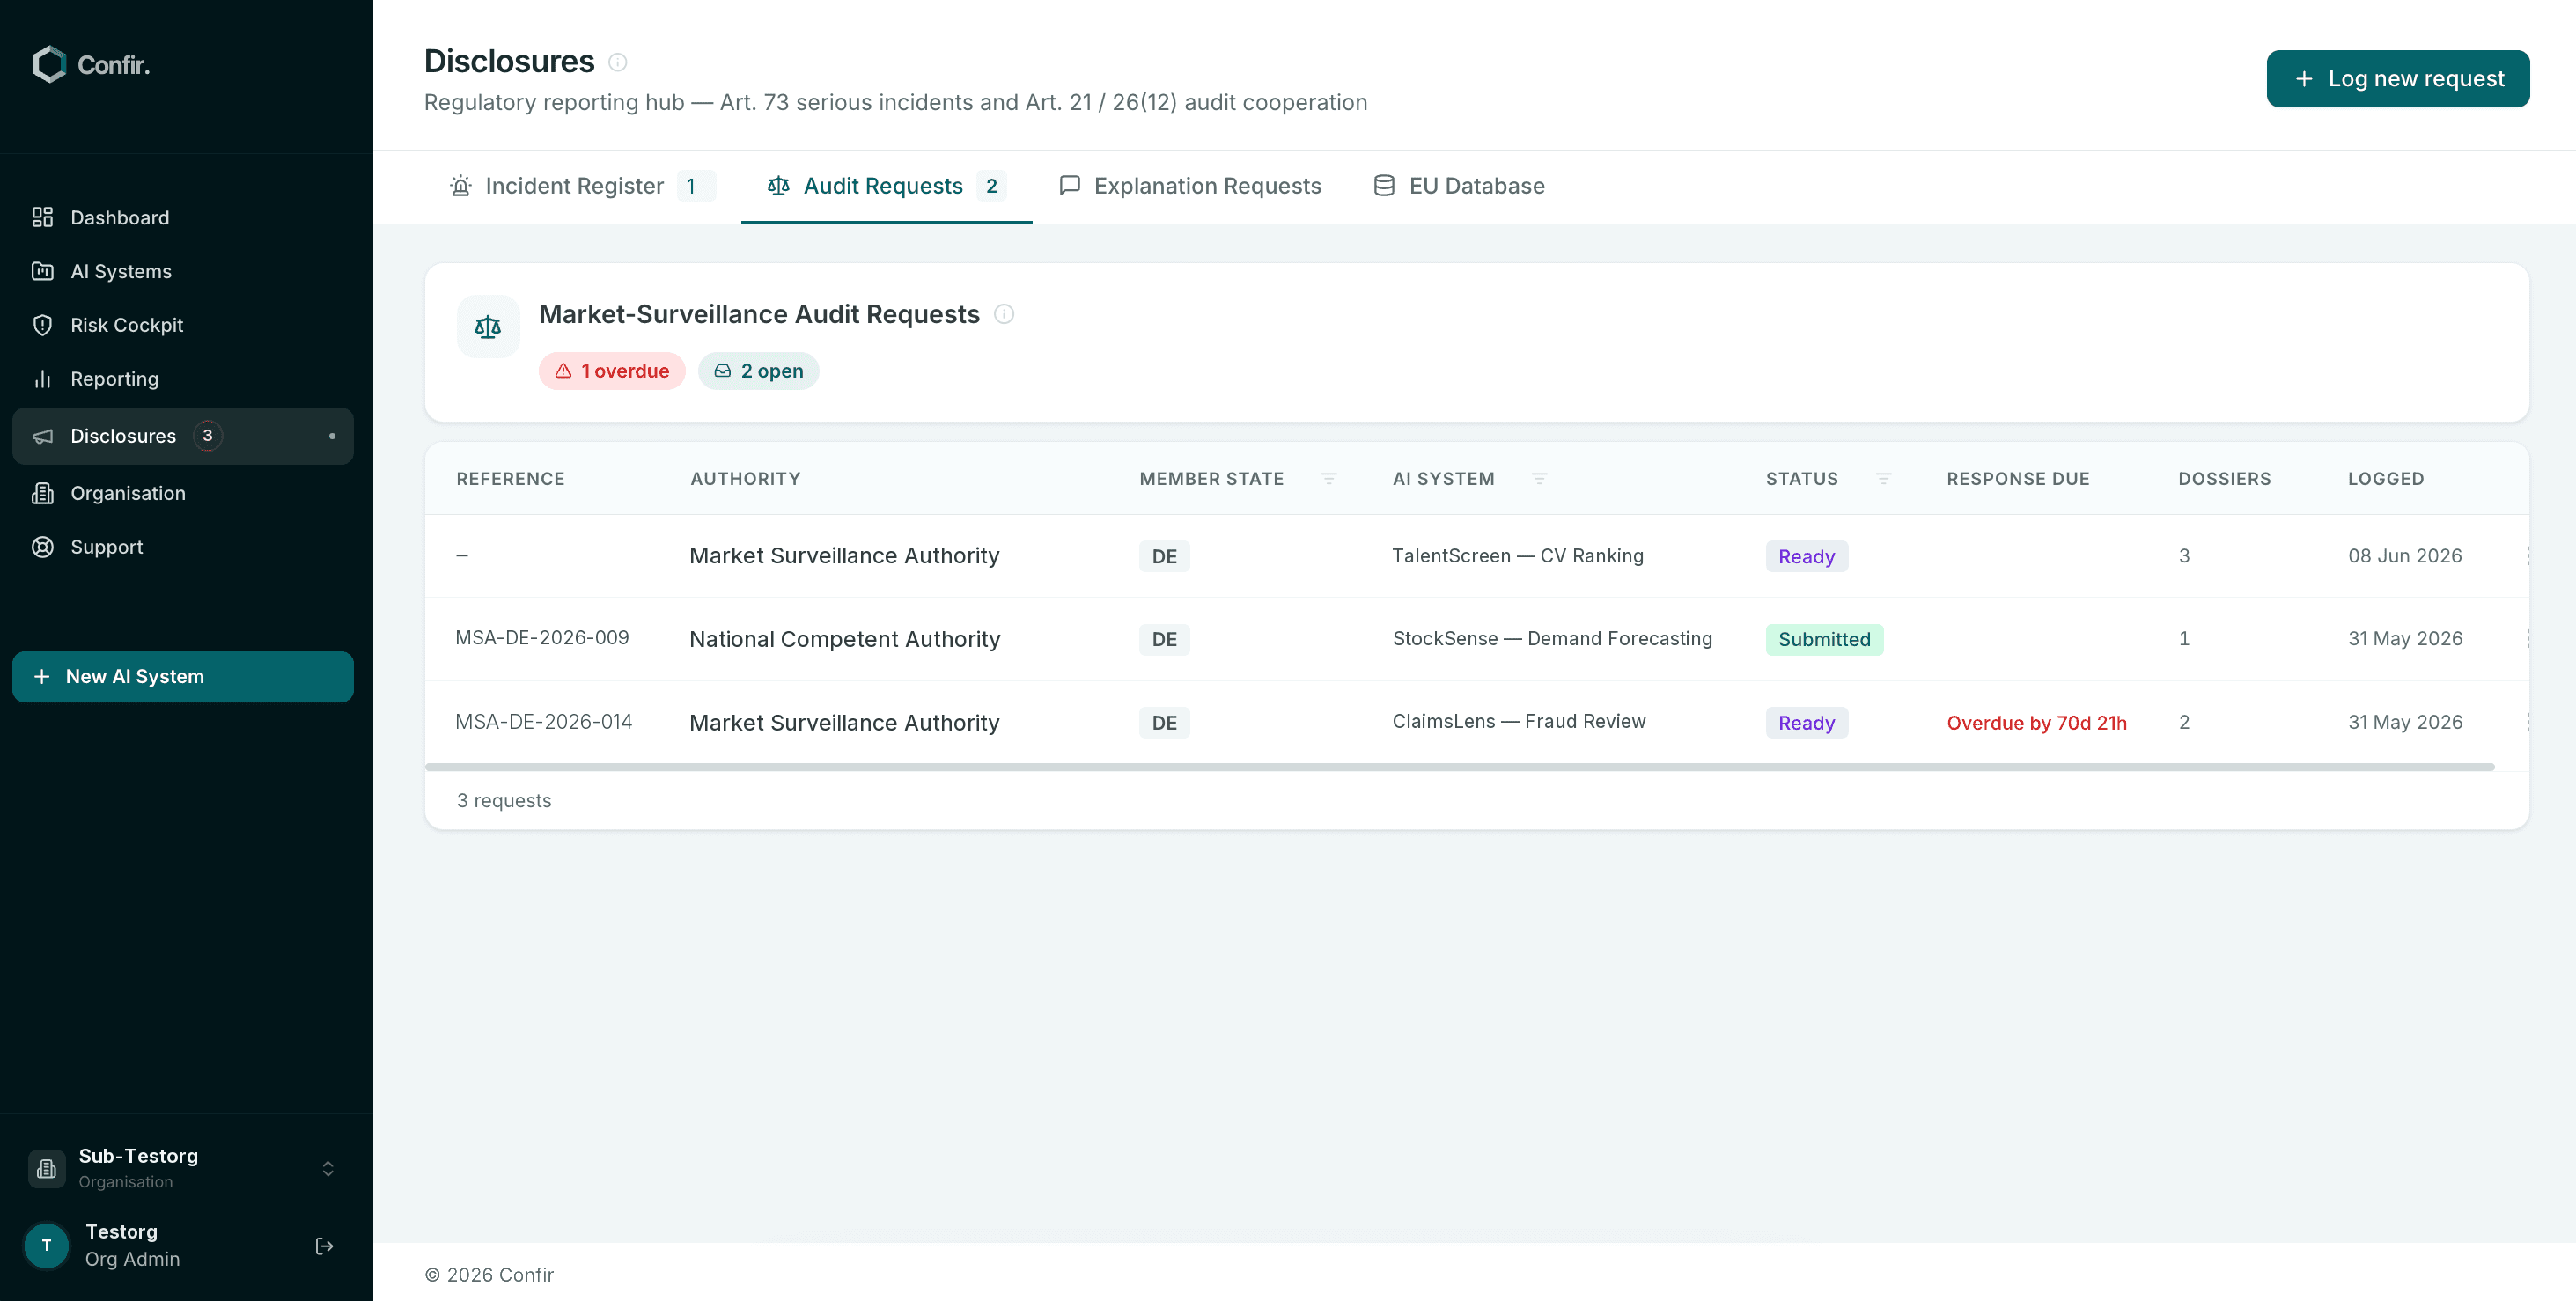
Regulatory disclosures & requests
Serious incidents, market-surveillance audit requests and Article 86 explanations, filed from one Disclosures Hub — each on its own deadline clock.
Every assessment, status, risk rating and finding is produced by transparent rules — no AI, no inference, no black box.
Tour the platformAI risk management: findings, health scores and reviews in one cockpit.
Three lenses on the same live data — system health, open findings and post-market reviews. Switch between them without leaving the screen.
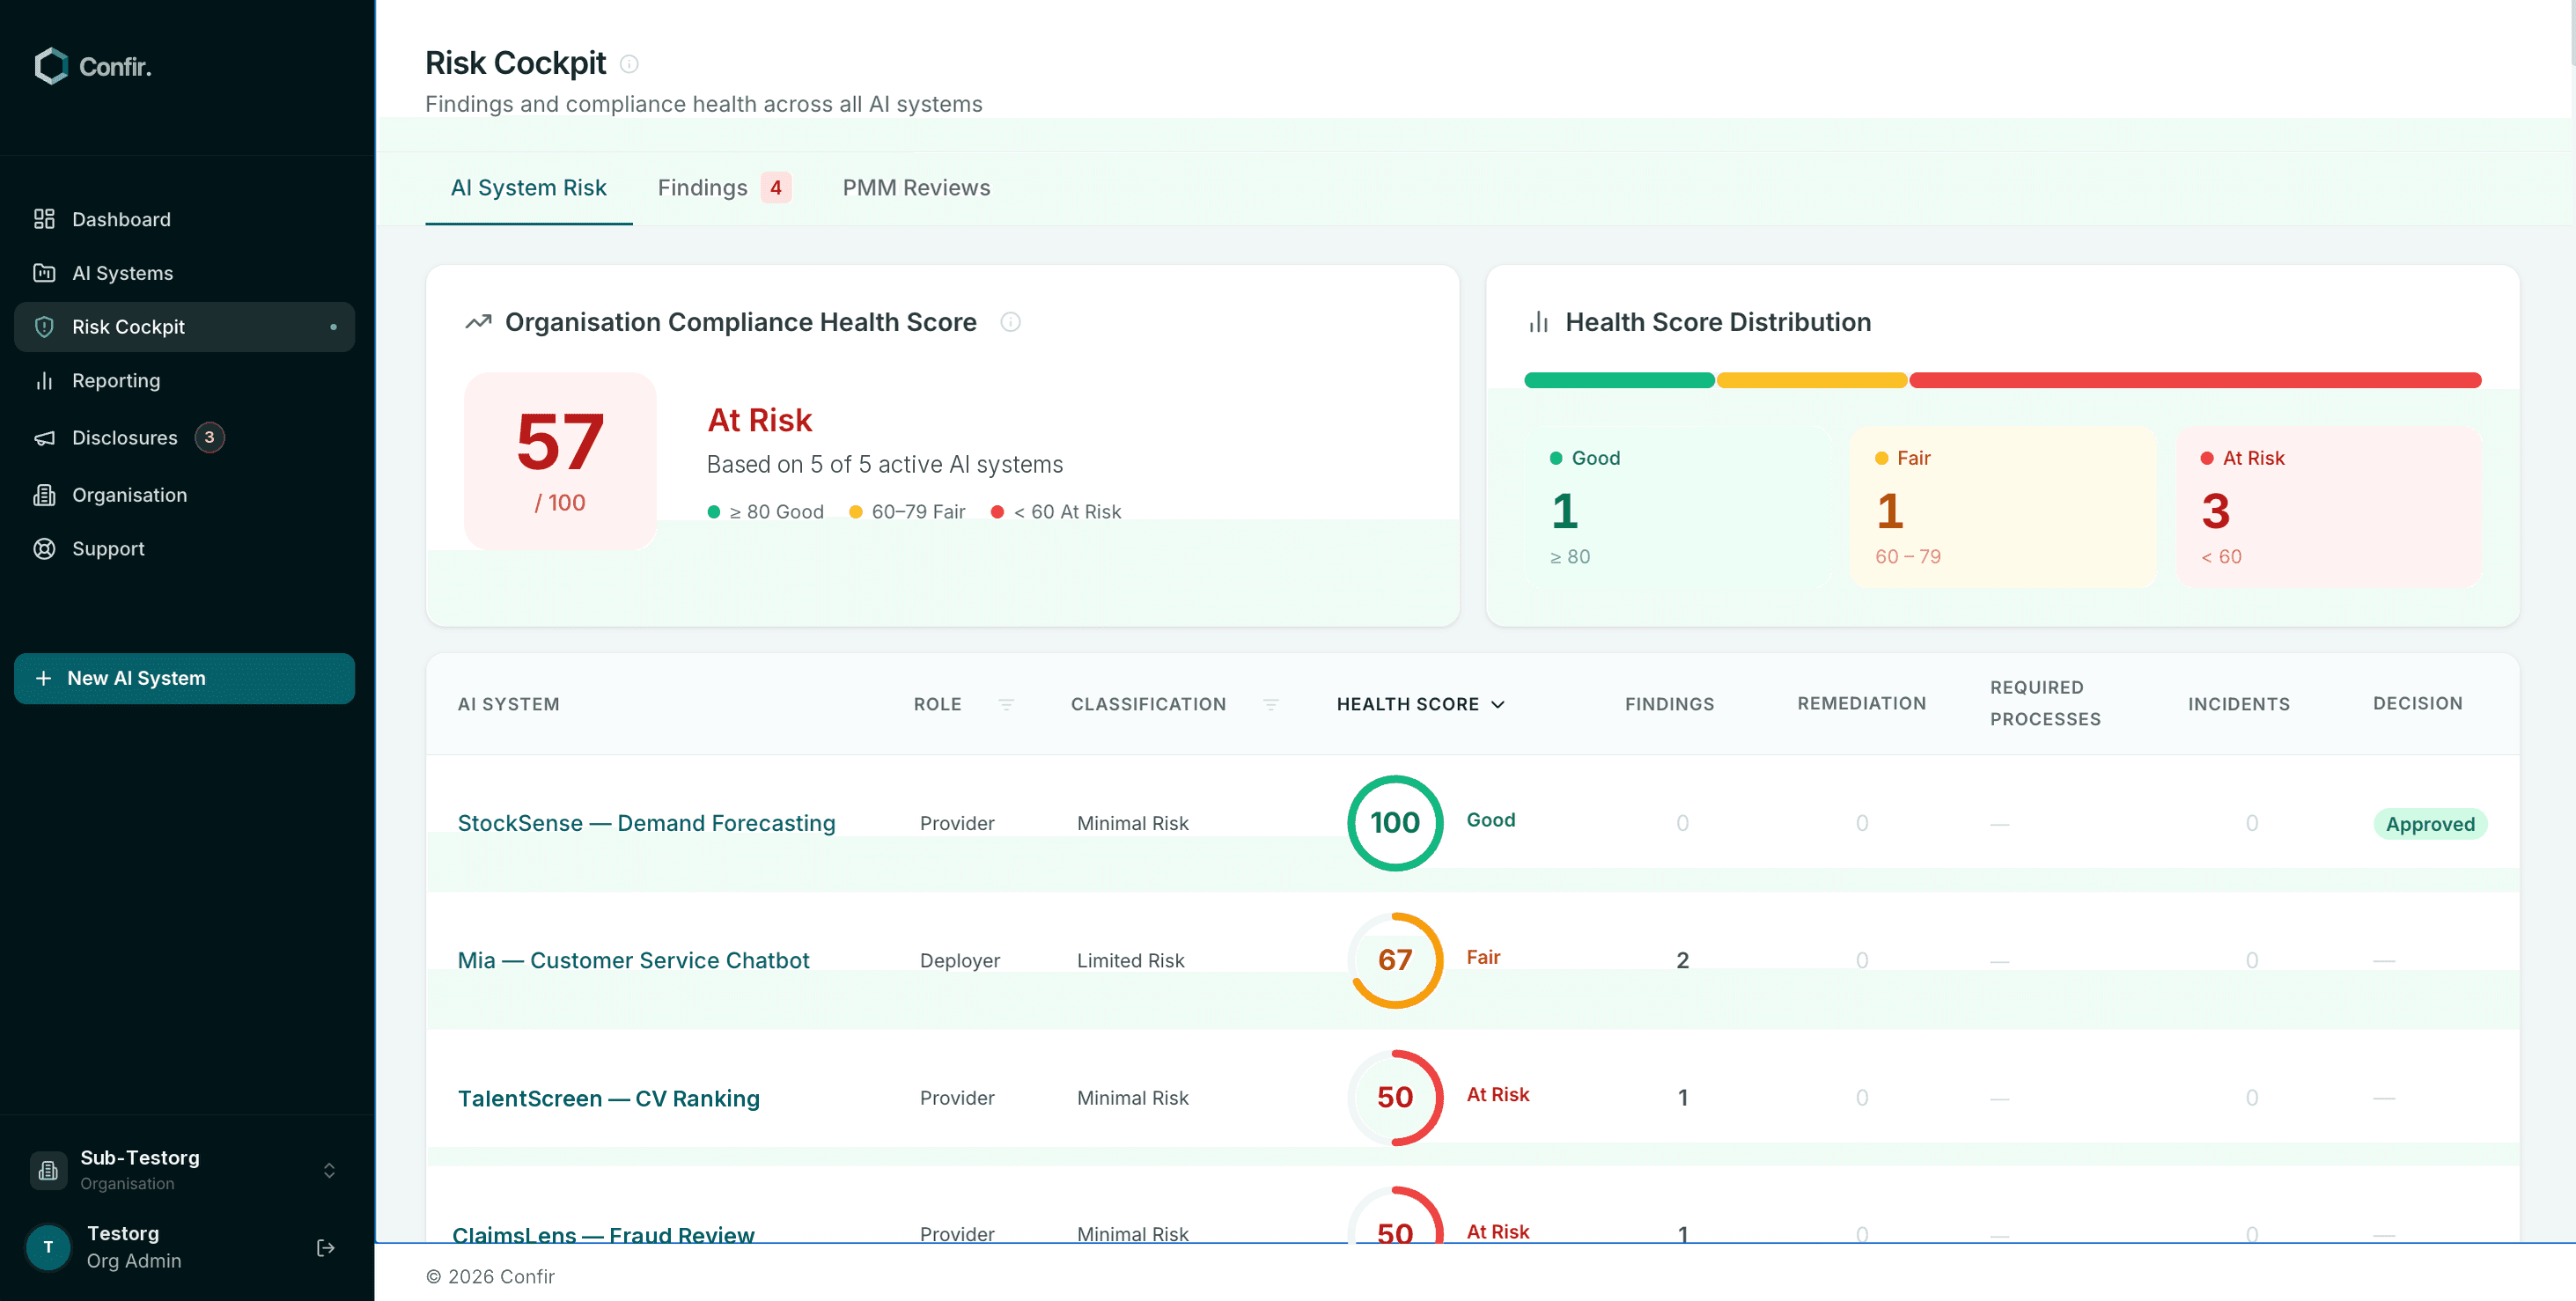
A live compliance health score for every AI system.
Each AI system carries one compliance Health Score, rolled up into a single organisation-wide number. Scores are built from open findings, overdue tasks and stale assessments, and colour-coded so leadership reads the posture at a glance while risk managers see exactly where to act first.
Organisation Compliance Health Score
Good
Fair
At Risk
TalentMatch AI — Candidate Screening
Deployer · High Risk
Real-Time Fraud Detection Engine
Deployer · High Risk
Live dashboards across your AI portfolio.
Portfolio size and coverage, the model categories behind each system and where control compliance stands across every domain. This is the same live reporting your auditor sees on inspection day: no nightly batch, no quarterly export.
AI Systems
13
High-Risk Systems
6
46% of portfolio
Portfolio Coverage
69%
9 of 13 systems assessed
GPAI-Driven
10
77% of portfolio
AI System Types
Distribution of AI model categories in portfolio
Control Compliance by Area
Assessment status across all domains
Explore each pillar in depth.
Enterprise-grade security,
EU-hosted by design.
Row-level database isolation, EU-only data residency, immutable audit logs and granular role enforcement. Security is an architectural requirement at Confir, not an afterthought.
Row-Level Security is enforced on every table. Queries are scoped to your organisation by database policy — not by application logic — so cross-tenant access is blocked at the lowest layer. Sensitive operations run server-side, and client code never touches raw database credentials.
Enterprise-grade security, EU-hosted by design.
Row-level database isolation, EU-only data residency, immutable audit logs and granular role enforcement. Security is an architectural requirement at Confir, not an afterthought.
Read the Trust HubFrequently asked, honestly answered.
Can't find what you're looking for? Browse our Support Center or reach out directly — we typically respond within one business day.
Assess your first AI system with Confir today.
Create your account, add your first AI system, and produce a full EU AI Act assessment with signed conformity documentation — in days, not months.